
Blog Content
Articles on knowledge, tools, and strategies needed to protect you and your stakeholders against evolving cyber threats.
Read moreEighty percent of the intrusions of your networks today can be handled by patches, anti-virus and user actions. We spend 90 percent of our time on the 80 percent of the issues that could be handled by good hygiene.

Your Trolling Definition is Wrong
It’s always good to keep your door open to constructive criticism when creating documents or anything else. Sometimes, you get amazing feedback, and sometimes, you just get noise. I’m sure you’ve experienced both ends of the feedback spectrum. I would like to share an…
Read moreSecurity breaches usually entail more recovery efforts than acts of God. Unlike proverbial lightning, breaches of security can be counted on to strike twice unless the route of compromise has been shut off.
Read moreIf security were all that mattered, computers would never be turned on, let alone hooked into a network with literally millions of potential intruders.
Read more“Do I want to know why you’re so informed about spyware?” she asked. Nikolaos gave her a charming, dazzling smile. “No, my dear. You do not.”
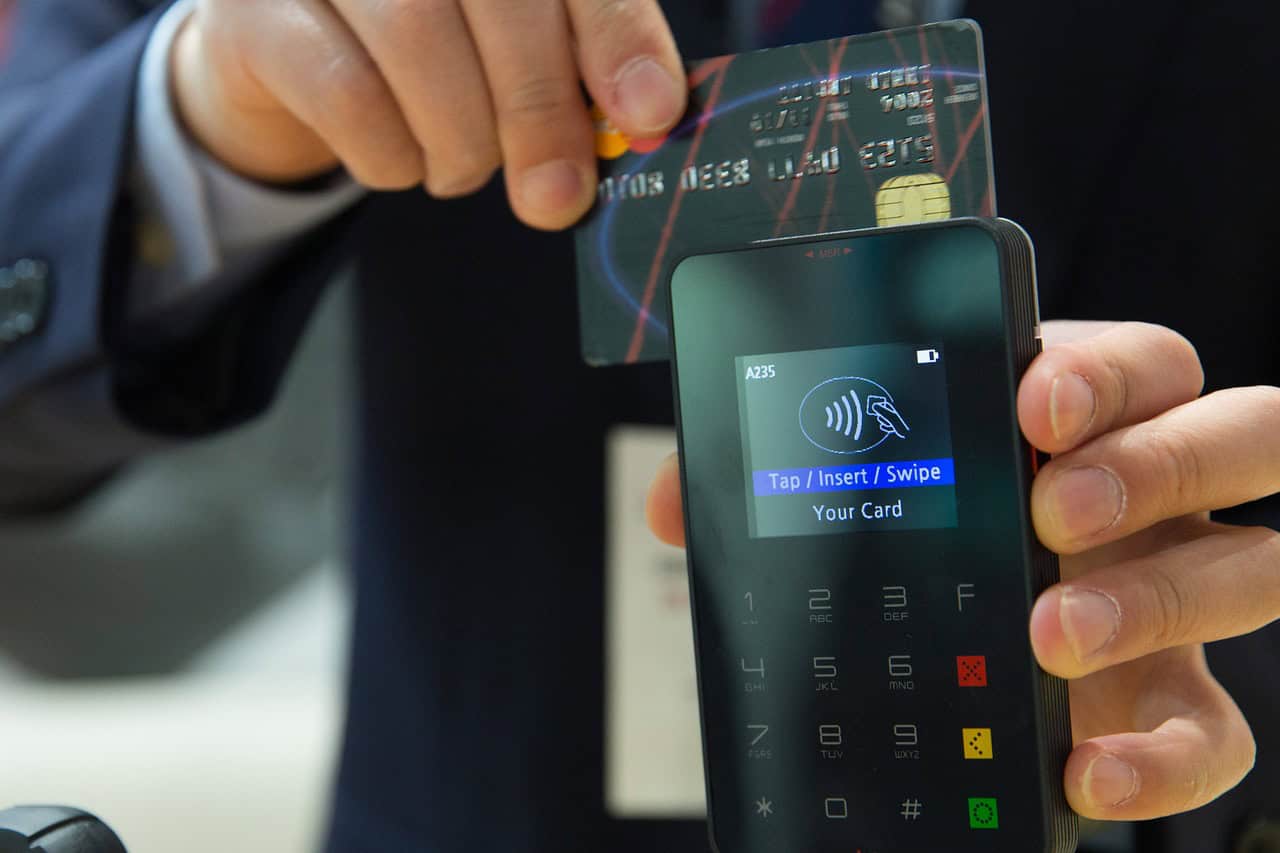
Exploring Regulated Information: PCI Data
PCI is the Payment Card Industry. The most common standard they provide is the PCI Data Security Standard (PCI DSS), which protects information that is considered PCI data. The basic premise is that all cardholder and sensitive authentication data must be protected….
Read moreWe didn’t install the [Code Red] patch on those DMZ systems because they were only used for development and testing [Shortly after spending 48 hours straight removing Code Red worm from internal corporate servers in 2001].

Exploring Regulated Information: HIPAA Data
HIPAA is the Health Insurance Portability and Accountability Act passed by Congress in 1996. HIPAA data is the information that would be covered under this act. Under this act are Protected Health Information (PHI) and ePHI, which can only be viewed by healthcare…
Read moreThe methods that will most effectively minimize the ability of intruders to compromise information security are comprehensive user training and education. Enacting policies and procedures simply won’t suffice. Even with oversight the policies and procedures may not be effective: my access to Motorola, Nokia, ATT, Sun depended upon the willingness of people to bypass policies and procedures that were in place for years before I compromised them successfully.

Exploring Regulated Information: CJIS Data
Next in line for the Exploring Series is exploring regulated information. That is information governed by law and punishable by fines or other sanctions if data breaches or compliance issues exist. This is a measure to get organizations to protect data that belong in…
Read moreTo competently perform rectifying security service, two critical incident response elements are necessary: information and organization.
Read moreIf you spend more on coffee than on IT security, you will be hacked. What’s more, you deserve to be hacked.
Need Additional Guidance?
Get recommended materials and more on the Resources Page.